Operating System
Data breaches cost businesses billions annually, yet most security failures stem from internal vulnerabilities. These 10 internal safeguards implement a zero-trust framework to lock down company data before threats escalate, blending technical controls with human-centric policies.
Role-Based Access Control Implementation
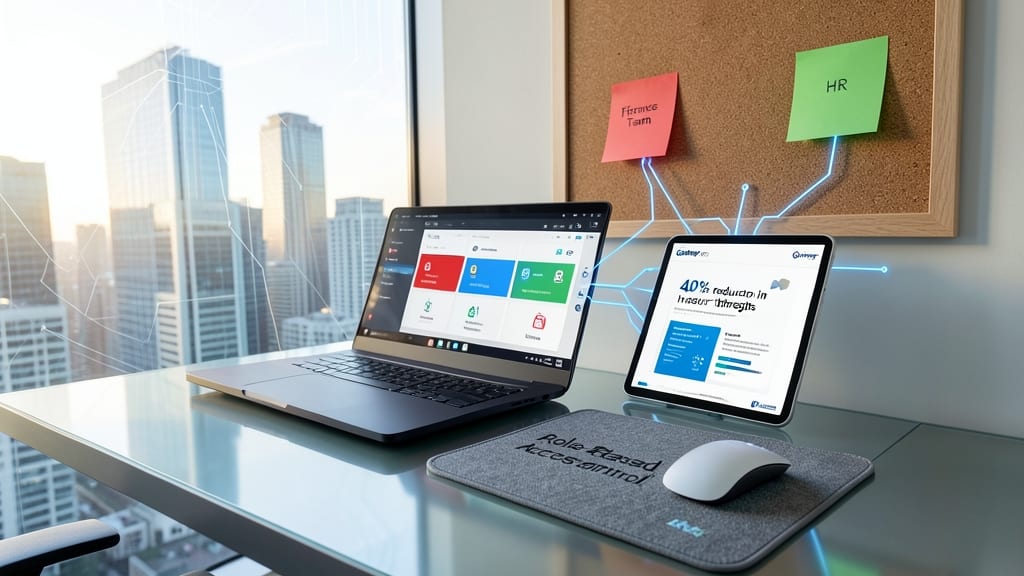
Tired of hearing about breaches caused by employees with too much access? Role-Based Access Control (RBAC) solves this by assigning permissions based on job functions—not trust levels. Gartner found it cuts insider threats by 40% by ensuring finance teams can’t access HR records, and developers can’t modify payroll systems.
Modern RBAC systems like Microsoft Azure AD or Okta let you define roles (e.g., "Marketing Editor," "IT Admin") with least-privilege access, auto-updating when employees change roles. Audit logs track every access attempt, and integration with Single Sign-On (SSO) streamlines adoption. The key is granularity: restrict access to specific folders, not just entire systems.
Perfect for mid-sized businesses with 100+ employees where IT teams lack time for manual permission reviews. Start with your most sensitive departments (HR, legal) to prove ROI before rolling out company-wide. 💻
Multi-Factor Authentication Enforcement
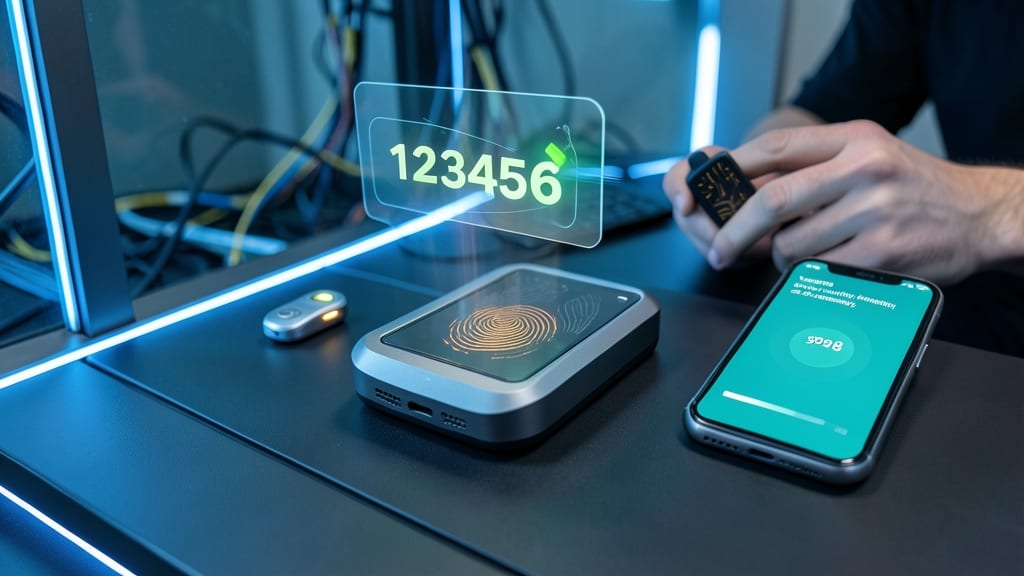
Tired of relying solely on passwords that take seconds to crack? Multi-Factor Authentication (MFA) enforcement adds an impenetrable layer by requiring hardware tokens, biometrics, or one-time codes—blocking 99.9% of automated credential stuffing attacks before they even reach your systems.
Modern solutions like YubiKey or Windows Hello for Business integrate seamlessly with Active Directory or Okta, enforcing MFA for VPN access, admin portals, and financial systems. Even a simple FIDO2 security key (costing under $20) can neutralize 90% of phishing attempts by eliminating SMS-based 2FA vulnerabilities.
Ideal for finance, healthcare, and legal teams, where data breaches carry severe penalties, MFA transforms weak passwords into a fortress wall. Start with critical systems—your IT team will thank you later. ✨
Data Loss Prevention Software Deployment
Forget firewalls and encryption alone—Data Loss Prevention (DLP) software acts as your company’s digital bouncer, stopping sensitive data from walking out the door before it happens. Unlike reactive security tools, DLP uses AI-driven pattern recognition to flag and block leaks in real-time, whether it’s an employee accidentally emailing client lists or a malicious insider exfiltrating trade secrets.
Top solutions like Symantec DLP or Microsoft Purview scan emails, cloud storage (OneDrive/SharePoint), and endpoints for predefined data patterns (credit card numbers, SSNs, PII). They even monitor USB transfers and print jobs—yes, that fax machine in accounting can still be a risk. The best systems integrate with SIEM tools for automated incident response, reducing mean time to containment from hours to minutes. Deployment is surprisingly straightforward with zero-config templates for common industries (healthcare, finance, legal).
This is the safeguard for teams handling highly regulated data (HIPAA, GDPR, SOX) or businesses where human error is the top risk. Start with email and cloud monitoring—the quickest win—and expand to endpoints as your security maturity grows. 💡
Regular Security Awareness Training Programs
Your employees might have the best firewalls and encryption in place, but the weakest link often sits right at their desks. Security awareness training programs turn your team into a human firewall, cutting phishing susceptibility by 70% through realistic simulations and compliance tracking.
These programs go beyond basic cybersecurity lectures by deploying phishing simulations that mimic real-world threats, then provide personalized feedback. Platforms like KnowBe4 or PhishMe track progress over time, ensuring repeated training sticks. The best programs also include gamified modules—like quizzes with leaderboards—to keep engagement high while reinforcing best practices.
Ideal for teams of all sizes, these programs are especially critical for industries handling sensitive data (healthcare, finance). Start with quarterly simulations and compliance checks to build a culture where security awareness becomes second nature. 💪
Endpoint Detection and Response Systems
While firewalls and antivirus block known threats, endpoint detection and response (EDR) systems act like cybersecurity bodyguards for your devices. They continuously monitor endpoints—laptops, servers, and IoT devices—for suspicious behavior, like unauthorized lateral movement where attackers hop between machines after breaching one.
Leading solutions like CrowdStrike Falcon or Microsoft Defender for Endpoint provide real-time behavioral analysis, threat hunting capabilities, and automated response actions. For example, if an attacker tries to exfiltrate data via PowerShell scripts, EDR can isolate the device and alert your team instantly—before sensitive files leave your network.
This is the ideal safeguard for organizations handling high-value data (financial records, intellectual property) or operating in regulated industries like healthcare. ⚡
Secure Document Management Policies
Forget hoping employees "remember" to share the right document versions—automated document management enforces security at the file level. Tools like Microsoft Purview Information Protection or Veeam Backup & Replication automatically classify files (e.g., "Confidential," "Public") and lock down access based on metadata, not just user roles.
With version control integration, you track every edit, deletion, or unauthorized share attempt—even in cloud storage like SharePoint or Dropbox. AI-driven classification flags sensitive data (SSNs, PII) and applies retention policies automatically, while audit logs show who accessed what and when. This isn’t just backup; it’s a digital vault that adapts to compliance needs (GDPR, HIPAA) without manual tagging.
Perfect for legal, finance, or healthcare teams where document integrity is non-negotiable. Even small businesses can deploy lightweight solutions like Box Governance or Google Vault to match enterprise-grade protection. 💻
Network Segmentation Architecture
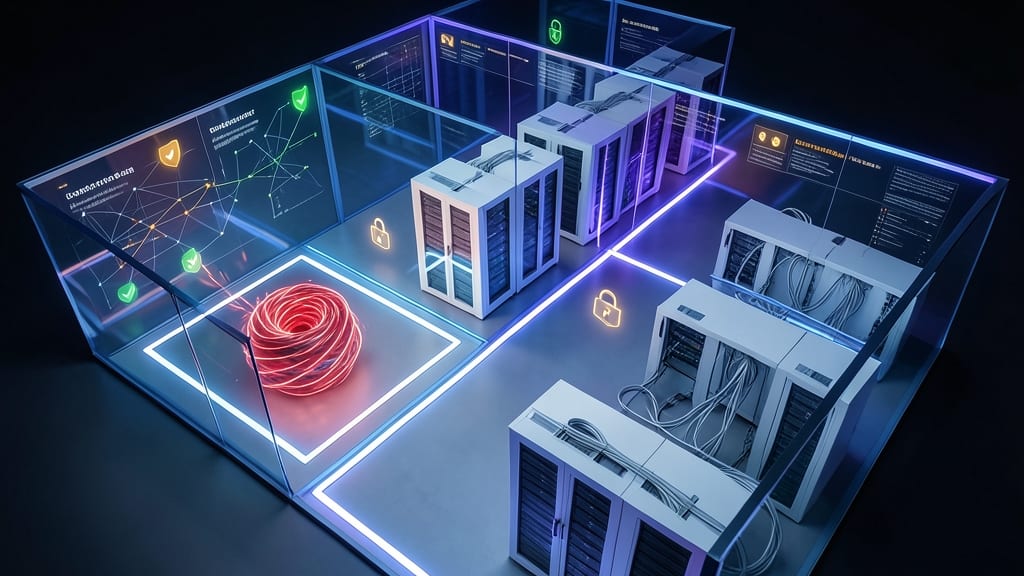
Imagine a breach happens—now picture it contained within a single department instead of spreading like wildfire across your entire network. That’s the power of network segmentation, where you divide your infrastructure into isolated zones to limit lateral movement and minimize damage.
This zero-trust approach uses micro-segmentation to create barriers between critical systems (like HR databases or financial servers) and general corporate traffic. Tools like Palo Alto Networks VM-Series or Cisco ACI dynamically enforce these rules, ensuring even compromised devices can’t hop between segments. The result? A 90% reduction in breach impact (per Forrester) by design, not just luck.
Perfect for enterprises handling sensitive data—especially healthcare, finance, and government sectors—where compliance meets strict security demands. Start with high-value assets first, then expand segmentation to legacy systems. 🌟
Third-Party Risk Assessment Protocols
Your company’s data isn’t just at risk from internal threats—it’s vulnerable through every third-party vendor you rely on. From cloud providers to SaaS tools, supply chain attacks now account for 60% of breaches, yet most businesses overlook vendor security until it’s too late.
Third-party risk assessment protocols solve this by combining standardized security questionnaires (like the ISO 27001 or NIST SP 800-160 frameworks) with continuous monitoring of vendors’ security posture. Tools like SecurityScorecard or BitSight automate vendor scoring, while contractual SLAs enforce compliance with real-time breach notifications. This approach catches vulnerabilities before they become your problem.
Ideal for businesses with 100+ vendors, these protocols are especially critical for healthcare (HIPAA compliance) and finance (PCI DSS requirements). Start with a risk-tiered assessment—prioritize vendors handling sensitive data over low-risk partners. ✨
Incident Response Simulation Drills
When a breach happens, every second counts—and quarterly incident response drills turn your team from reactive to proactive. These tabletop exercises simulate real-world attack scenarios (like ransomware or insider threats) to expose gaps in your playbook before they become costly mistakes.
Using tools like MITRE ATT&CK frameworks or custom-built war games, your team practices detecting threats faster and containing breaches with 50% improved response times (per NIST studies). The drills include mock alerts, escalation procedures, and even PR crisis simulations—all while measuring how quickly teams isolate affected systems or restore backups.
Ideal for mid-sized to large organizations, these exercises are most valuable when tied to real-time metrics tracking. Even small teams can start with low-cost, high-impact scenarios like phishing simulations paired with response drills. 💪
Continuous Vulnerability Scanning Programs
Imagine discovering a critical security flaw in your systems—before hackers even know it exists. Continuous vulnerability scanning programs do exactly that by automating penetration testing, simulating real-world attacks to uncover weaknesses in real time.
These tools, like Nessus Professional or OpenVAS, scan networks, applications, and endpoints 24/7 using CVE databases and custom rule sets. They prioritize risks by severity, integrate with ticketing systems for zero-config patching, and even simulate OWASP Top 10 attack vectors. Unlike manual audits, they adapt to evolving threats, reducing exposure by up to 80% according to NIST benchmarks.
Perfect for mid-sized businesses to enterprises, these programs fit seamlessly into existing security stacks—especially when paired with your network segmentation or third-party risk protocols. The peace of mind? Knowing your defenses are always one step ahead. ⚡